Integrations

Harden Your Cisco SASE Controls

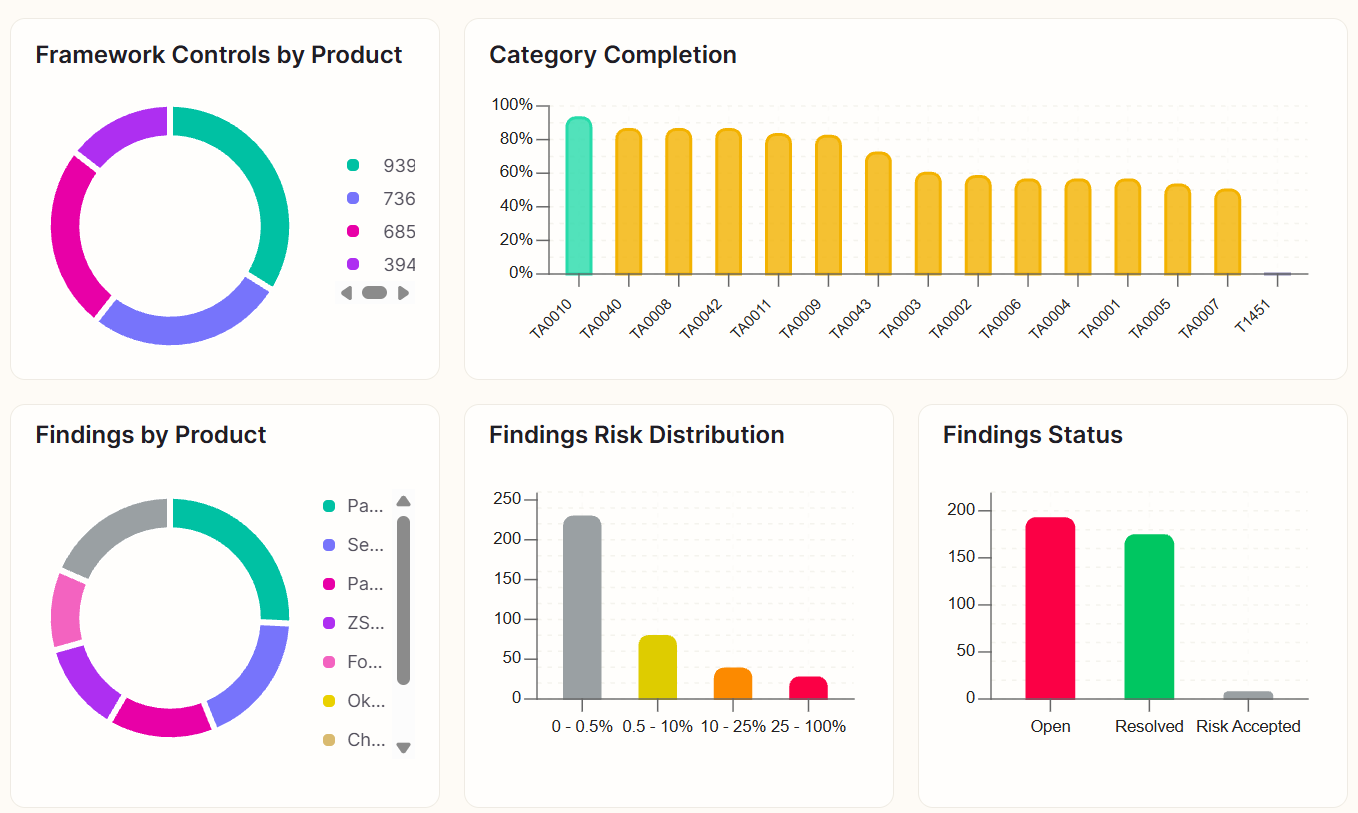
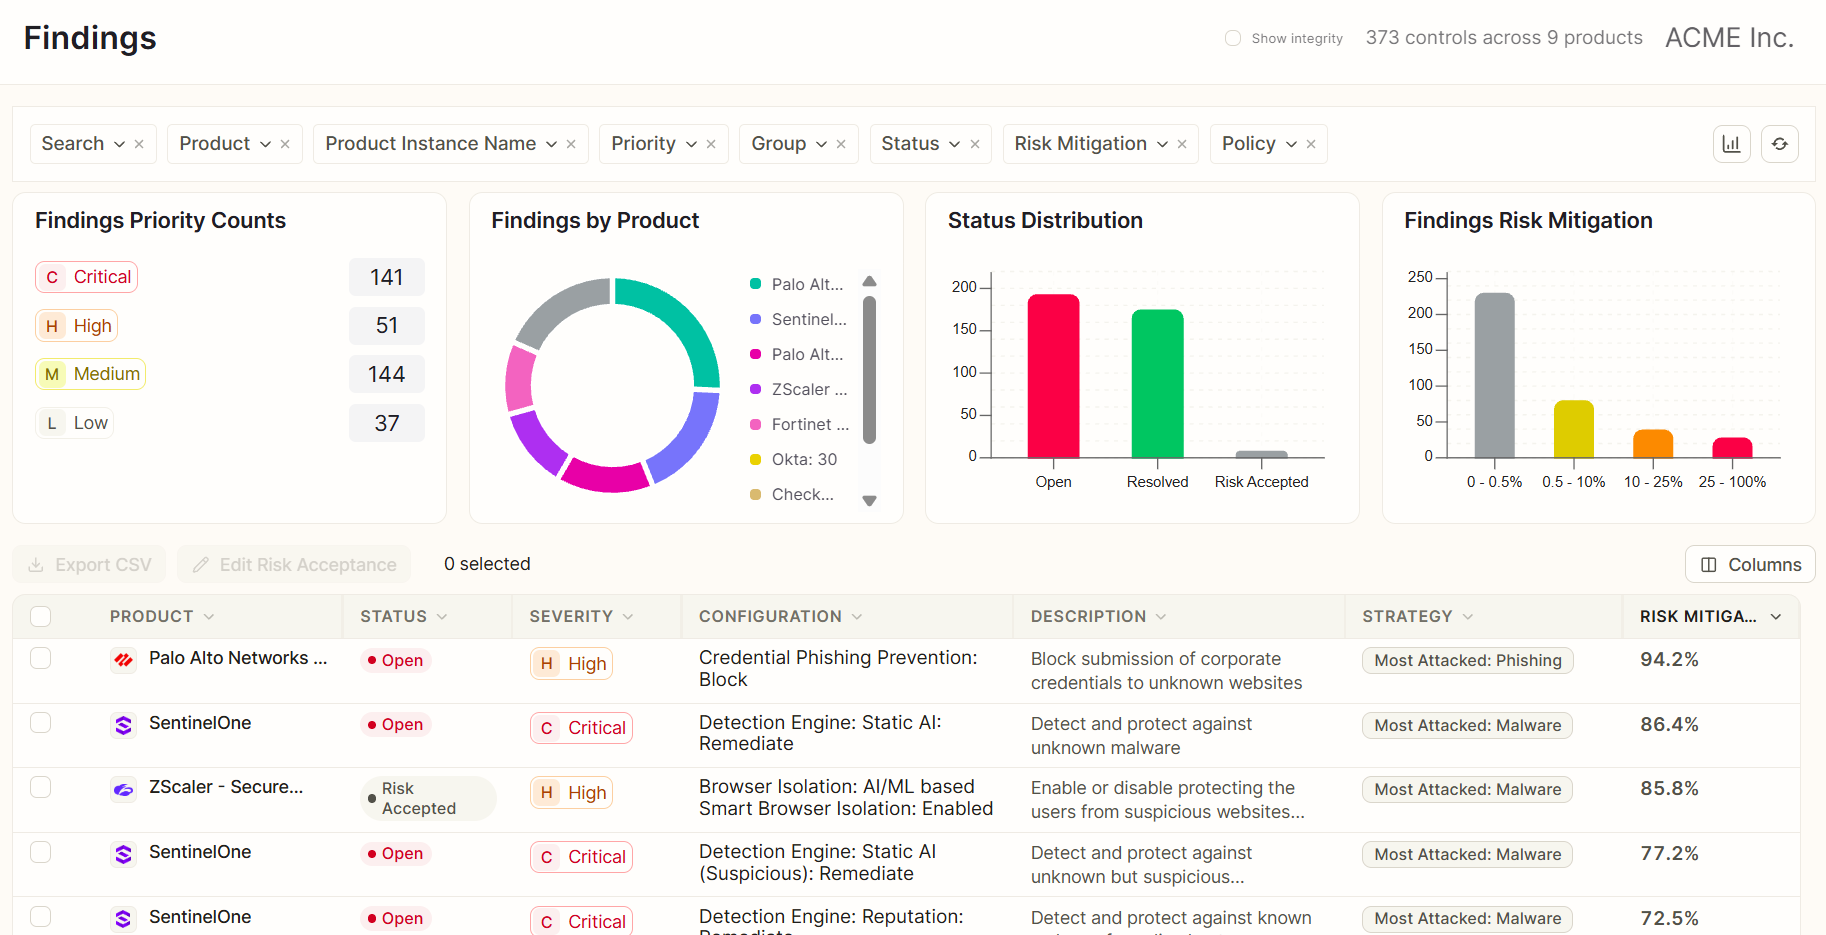
Reach analyzes your Cisco SASE deployment to find misconfigurations, policy gaps, and configuration drift across cloud-delivered security and access controls. Reach prioritizes fixes, activates underutilized protections, and continuously validates that Cisco SASE controls remain aligned with security policy.
Cisco SASE

The Challenge

Cisco SASE brings together secure connectivity, cloud security, and Zero Trust access across users, devices, applications, branches, and cloud environments.

#AAA8A0

#201F1C

32

Inter

center

But as Cisco SASE policies evolve, configurations can drift from their intended state.

Reach continuously analyzes Cisco SASE controls to identify incomplete inspection controls, overly permissive access, weak device trust, and inconsistent policy enforcement. Reach can then remediate misconfigurations, activate unused capabilities, and validate that protections stay aligned with security intent.

Align SD-WAN and Secure Access Policies
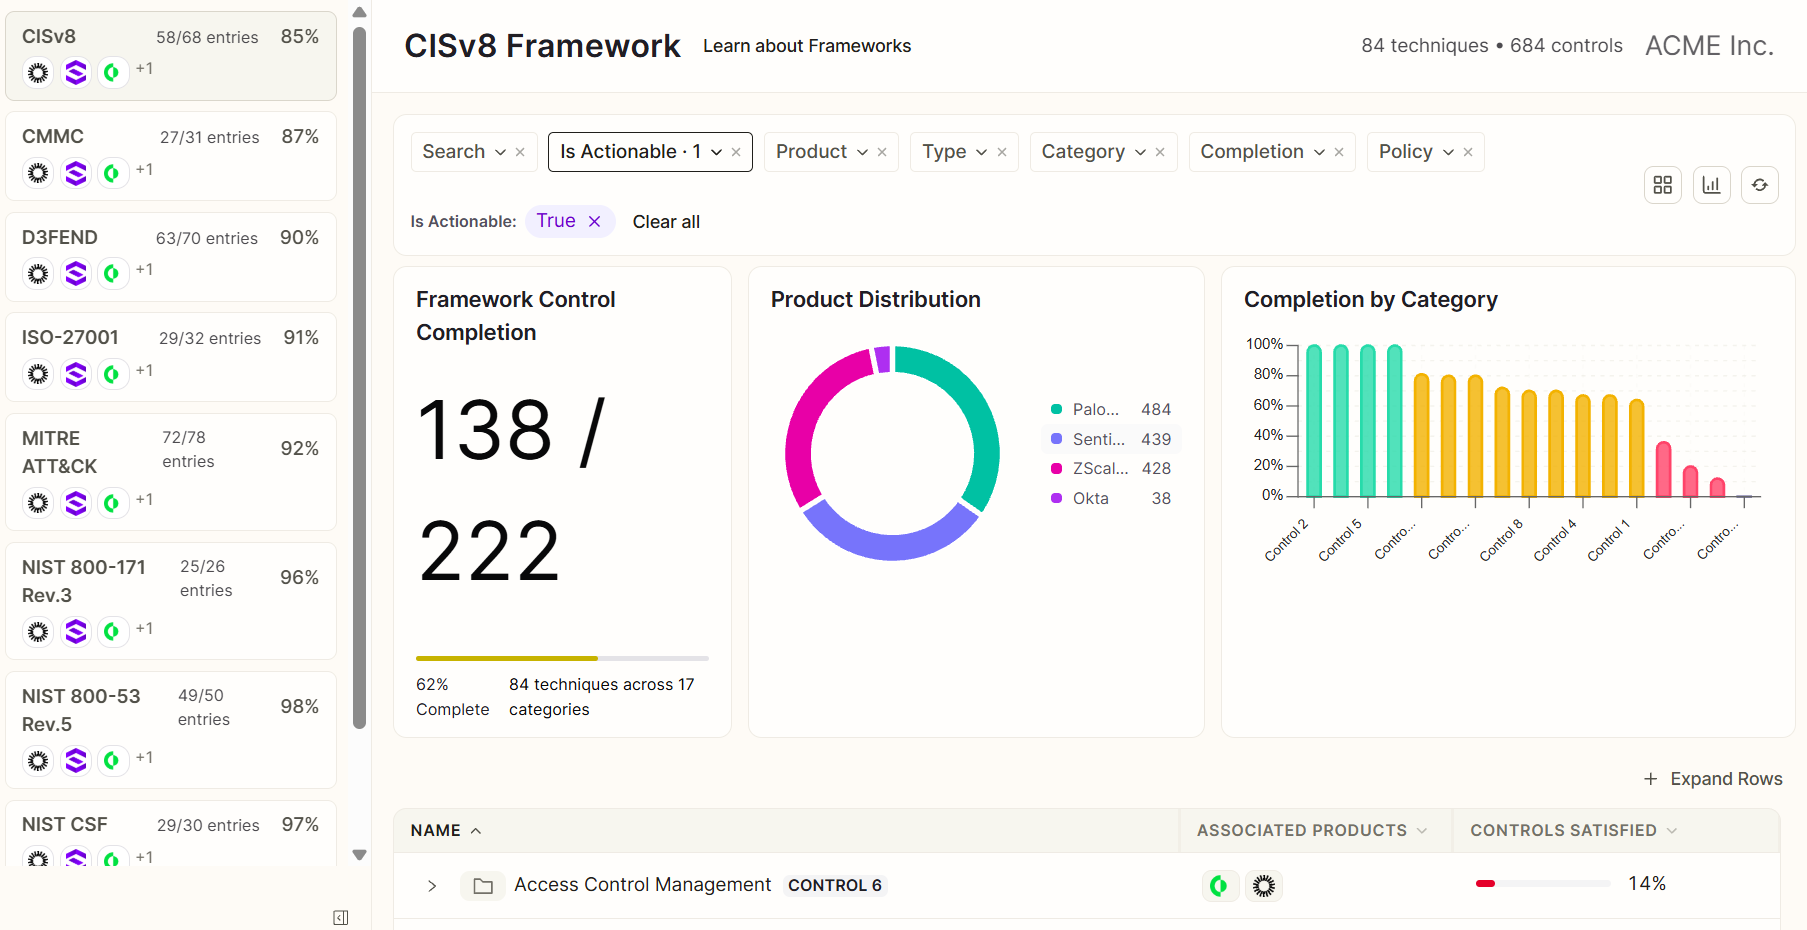
Cisco SASE uses SD-WAN and Secure Access policies to connect users, branches, and cloud environments to applications. Reach analyzes policy alignment across users, locations, and applications to identify inconsistent enforcement, risky access paths, and drift from intended security posture.
Tighten Umbrella DNS, SWG, and Firewall Controls
Cisco Umbrella delivers DNS-layer security, Secure Web Gateway, cloud-delivered firewall, and CASB controls as part of Cisco’s SASE architecture. Reach analyzes these configurations to identify overly permissive rules, inspection gaps, and policy exceptions that weaken protection. By tightening these controls, Reach helps block malicious domains, risky web traffic, and unauthorized outbound connections.
Enforce Zero Trust Access and Device Trust
Cisco Secure Access and Duo help enforce identity-first Zero Trust access using MFA, device visibility, adaptive policies, and device health checks. Reach analyzes access policies to identify weak authentication requirements, missing device posture checks, and overly broad application access. This helps ensure only trusted users and healthy devices can access sensitive resources.
Validate Policy Drift Across Cisco SASE
Cisco SASE spans multiple control planes across networking, cloud security, access, and observability. Reach continuously monitors configuration changes across these controls to detect drift before it weakens security posture. When policies move away from baseline, Reach surfaces the issue and guides remediation to restore consistent protection.

Other integrations

View All

decorativedecorative

Getting Started with Reach

Unlock the full power of your security stack with a free tool rationalization assessment.

Request a Demo

An API key to start

Read-only API key for a security tool of your choice

Setup in 3 minutes

Create your account and setup the integration

Results in < 5 days

Get results across licensing, control mapping, risk exposure, and posture

Think your firewall is secure? Find the 10 weaknesses attackers look for

Get the free checklist

decorativedecorative